The Company
Authentication built the session. We build the act.
We build one thing: a sensitive action does not run until it carries authority a person signed, on their own device, for that action.
Founder
The observation that became the company.
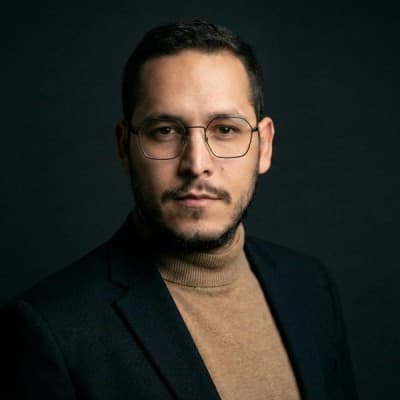
Mohamad Khalil Yossif
Founder & CEO
Yuthent started from a real problem I hit building a workforce product. Customers refused to give up on-site biometric check-ins. Not because they liked biometrics, but because everything else could be handed over: a password, a code, a badge, a session. The press was the part that stayed with the person.
That observation generalized. Every industry facing social engineering, insider abuse, session hijacking or agent delegation runs into the same gap, and the existing stacks answer it with a session token. Yuthent answers with the press itself.
“A valid session is not proof of approval. A signed action is.”
What we have built
Concrete. Operating. Shipping today.
Native SDKs for Android and iOS
The signing key is generated inside the phone's secure hardware, Android's StrongBox or the TEE or the iOS Secure Enclave, and released by the person's fingerprint or face. Signing needs no network, with a durable queue on the device for what has not synced yet.
The control plane
The screen a customer's own team runs it from: the device fleet and its health, the trust policy, alert triage, the record of what people approved, device revocation, webhooks into their SIEM and a daily audit export.
The backend that enforces the contract
The service that verifies an approval before it counts, refuses a repeat, and keeps the record of what a person approved. What that record does and does not settle is set out in full on the security page.
Link-enrollment grant flows
In-person and video-remote link enrollment. Time-boxed, scoped, signed grants. The pieces under patient consent, supervised onboarding and field-operator workflows.
Standing
What the company stands on.
The category is specified in the open.
Yuthent authors and publishes draft-yossif-psea-02, the Internet-Draft that specifies it, and the approval-integrity requirement merged into OWASP AISVS 1.0. The draft is an individual submission: not adopted by an IETF working group, and not IETF consensus. The repository is public.
The specification is open. The implementation is ours.
Publishing the category is deliberate: a thing nobody can read is a thing nobody adopts. The authorization method and the device-bound execution-proof architecture behind it are the company's own work.
Selected.
By SafeNology (Takwin Ventures and S.T-Impact) and by Hasoub Labs, Cohort 4.
See it on your own flow.
Your app, your call, our SDK.